Qué mira, y con qué lo contrastaWhat it watches, and what it checks it against
Cada señal viene de una fuente concreta y se dice cuál. Es una herramienta defensiva y forense — para inspeccionar tu propia máquina.Every signal comes from a named source, and it says which. A defensive, forensic tool — to inspect your own machine.
Conexiones y procesosConnections & processes
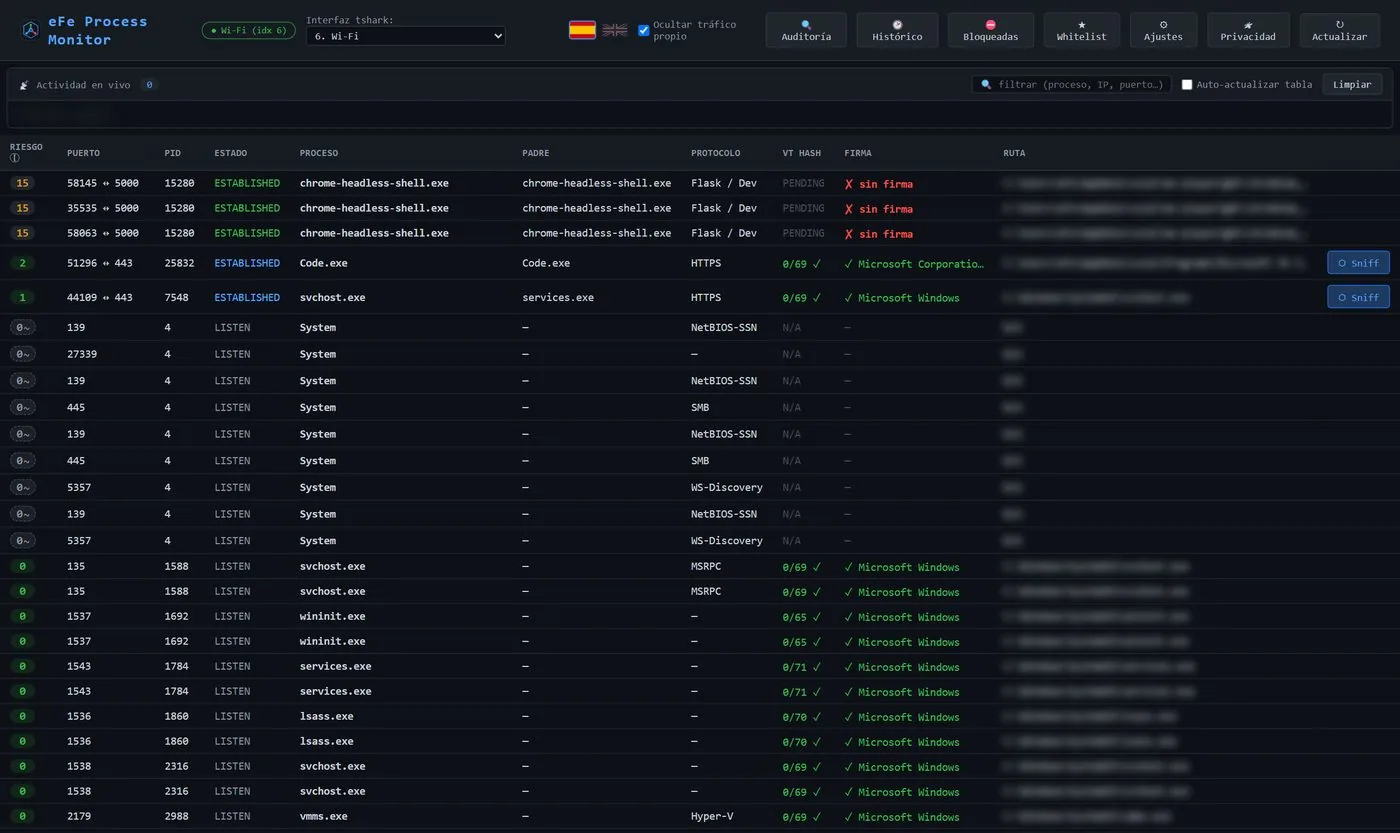
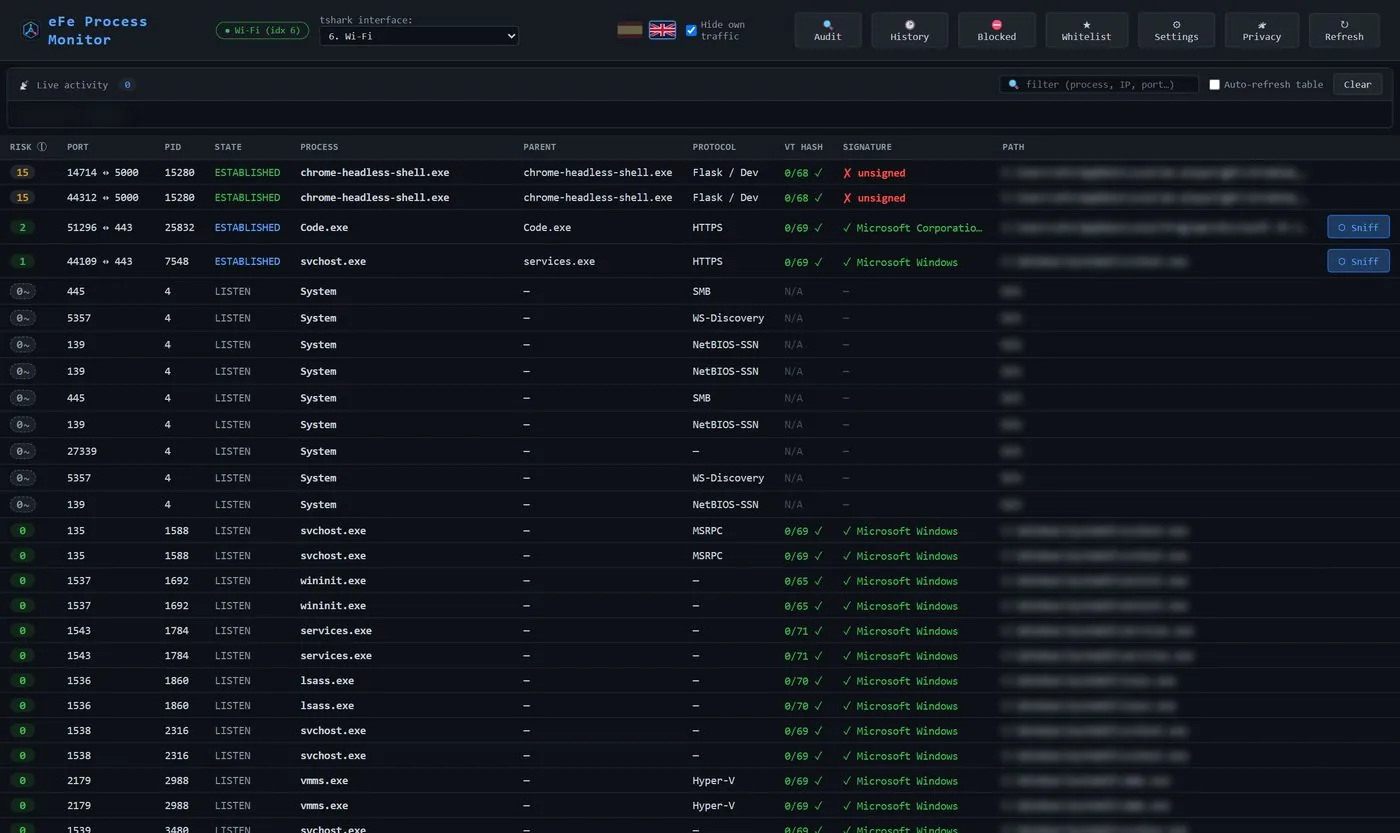
Cada conexión con su proceso: padre, línea de comandos, hora de inicio, I/O. Y la cadena de ancestros completa (powershell ← winword ← explorer), que marca cuando un documento o un navegador lanza un intérprete.Each connection with its process: parent, command line, start time, I/O. Plus the full ancestry chain (powershell ← winword ← explorer), flagging when a document or browser spawns an interpreter.
Reputación e inteligenciaReputation & intel
Binario por hash en VirusTotal + firma (Authenticode / paquete en Linux). IP por geo, rDNS y varias listas. Y lo que el proceso pidió de verdad: nombres desde el SNI de TLS y las respuestas DNS — más fuerte que el rDNS, que lo controla el dueño de la IP.Binary by hash on VirusTotal + signature (Authenticode / package on Linux). IP by geo, rDNS and several lists. And what the process actually asked for: names from the TLS SNI and DNS answers — stronger than rDNS, which the IP's owner controls.
Score de riesgo 0–100Risk score 0–100
Combina todas las señales, ordenable, con el desglose al pasar el ratón. Es heurístico y honesto: un valor bajo significa "sin señales", no "seguro"; lo incompleto se marca, y el ruido sobre grandes proveedores se atenúa.Combines every signal, sortable, with a per-signal breakdown on hover. It's heuristic and honest: a low value means "no signals", not "safe"; incomplete data is marked, and noise about big providers is damped.
En vivo: beaconing y caudalLive: beaconing & egress
Feed de conexiones y procesos nuevos, heurísticas de beaconing/C2 (llamadas regulares al mismo host), caudal de datos por proceso con marca de salida sostenida, y notificaciones de escritorio opcionales.A feed of new connections and processes, beaconing/C2 heuristics (regular calls to the same host), per-process data rate flagging sustained egress, and optional desktop notifications.
Captura de paquetesPacket capture
Por conexión, con tshark: SNI de TLS, host HTTP, DNS y flags, con exportación a pcap y detección automática de interfaz. Opcional.Per connection, with tshark: TLS SNI, HTTP host, DNS and flags, with pcap export and automatic interface detection. Optional.
Auditoría del equipoMachine audit
Comprobaciones de procesos sospechosos, persistencia, hardening e indicios de rootkit. Corre 100% en local. Y un histórico forense en SQLite con la cronología del riesgo: qué pinta tenía cada veredicto el martes.Checks for suspicious processes, persistence, hardening and rootkit hints. Runs 100% locally. Plus a forensic SQLite history with a risk timeline: what each verdict looked like last Tuesday.
Cada conexión, abiertaEvery connection, opened up
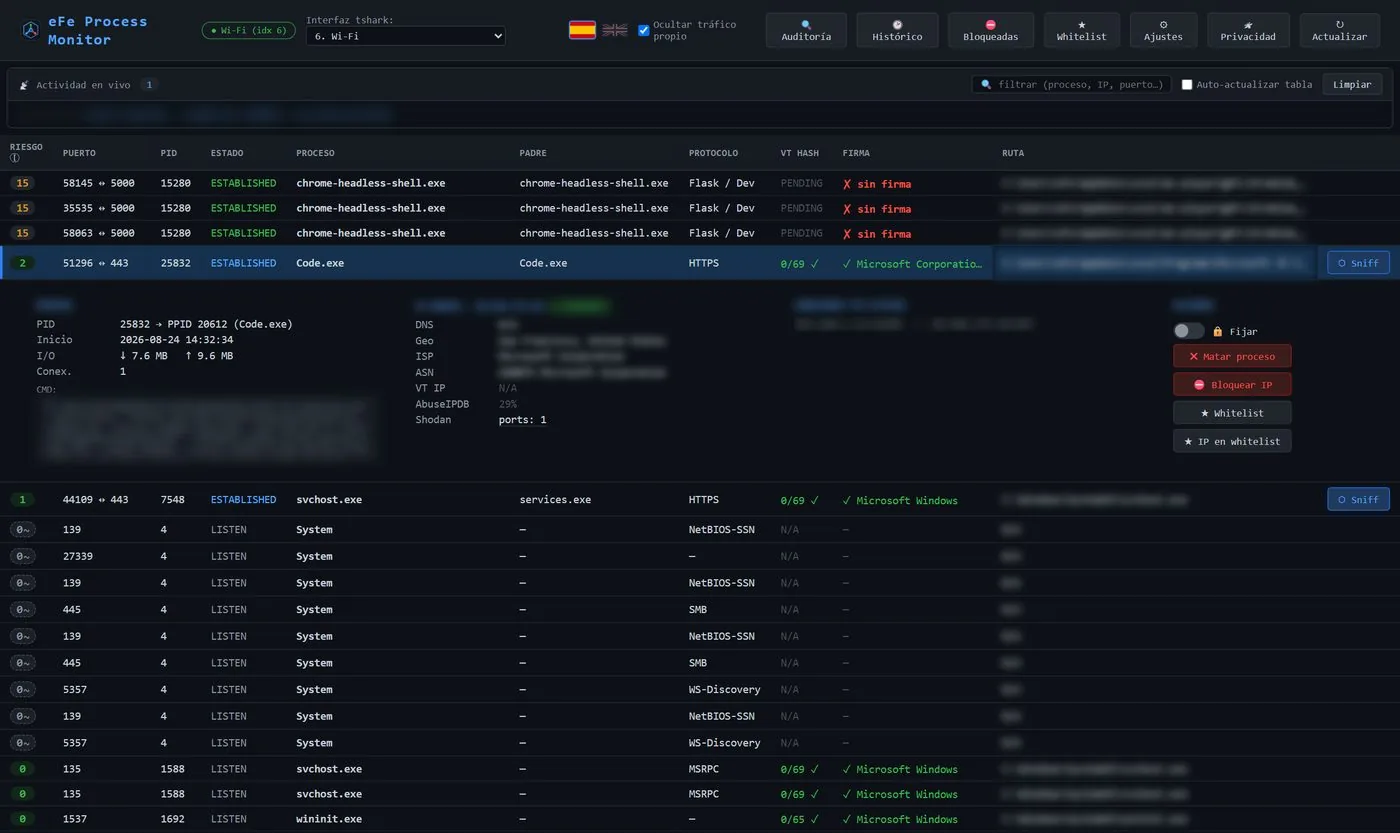
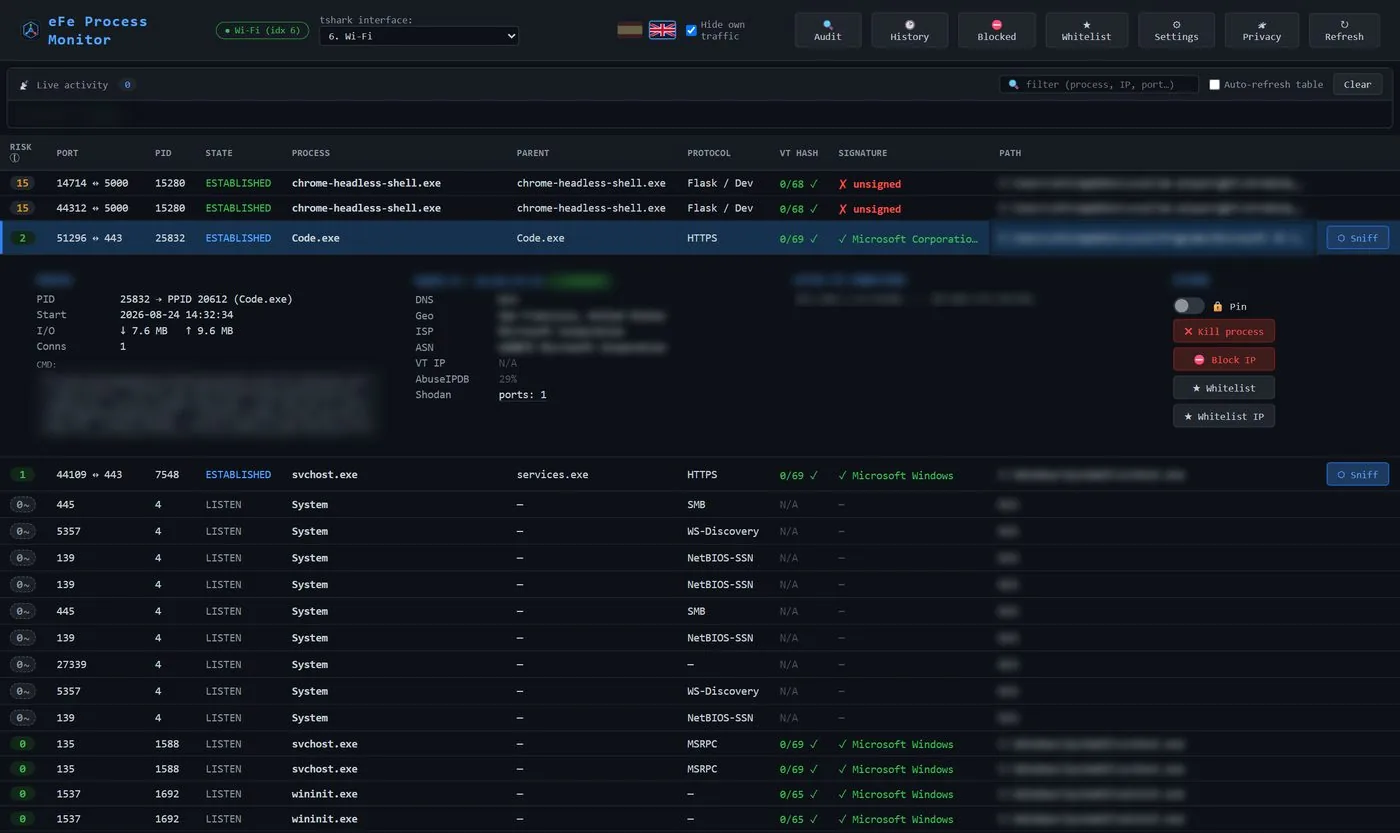
Un clic despliega la tarjeta: ancestría, I/O y caudal, y todo lo que las fuentes dicen de esa IP: VirusTotal, AbuseIPDB, Tor, Shodan, C2.One click opens the card: ancestry, I/O and rate, and everything the sources say about that IP — VirusTotal, AbuseIPDB, Tor, Shodan, C2.
PrivacidadPrivacy
Todo en local. Sin telemetría.Everything local. No telemetry.
Todo se guarda en tu máquina (efemon.db). No hay cuenta, ni nube, ni nada que se envíe "a casa".Everything is stored on your machine (efemon.db). No account, no cloud, nothing phoned home.
Solo lo que tú inspeccionasOnly what you inspect
Para enriquecer, consulta servicios externos solo sobre las IPs/hashes que tú miras (VirusTotal, AbuseIPDB, Shodan, ipwho.is). Las listas de abuse.ch/Spamhaus/Tor son descargas públicas que no revelan nada de ti. Todo se cachea.To enrich, it queries external services only about the IPs/hashes you look at (VirusTotal, AbuseIPDB, Shodan, ipwho.is). The abuse.ch/Spamhaus/Tor lists are public downloads that reveal nothing about you. Everything is cached.
Auditoría 100% localAudit runs 100% locally
La auditoría del equipo no consulta nada fuera. Y el panel 🛰 Privacidad de la propia app detalla exactamente qué sale y a dónde — sin letra pequeña.The machine audit queries nothing external. And the app's own 🛰 Privacy panel spells out exactly what leaves and where — no fine print.
Solo en tu loopbackLoopback only
Por defecto el panel escucha solo en 127.0.0.1, con un token de acceso local. Exponerlo a la red es opcional y exige contraseña + HTTPS. Con anti DNS-rebinding y anti-CSRF.By default the panel listens on 127.0.0.1 only, behind a local access token. Exposing it to the network is opt-in and requires a password + HTTPS. With anti DNS-rebinding and anti-CSRF.
DescargarDownload
Libre y de código abierto (MIT). Un binario, sin instalación.Free and open source (MIT). One binary, no install.
N/A). La captura de paquetes necesita tshark en el PATH. Las claves de VirusTotal / AbuseIPDB son gratis y opcionales. macOS no está soportado (compila, pero varias sondas de la auditoría no existen ahí — mejor no fingir que sí).Run it as administrator / root to see every process and use kill / block IP; it works unprivileged too (some show N/A). Packet capture needs tshark on PATH. VirusTotal / AbuseIPDB keys are free and optional. macOS is not supported (it builds, but several audit probes don't exist there — better than pretending they do).